AI Summary Powered by PixelBrainy
Can a 600-bed hospital realistically prove its AI, privacy, regulatory, and clinical governance status in real time when the evidence still lives across spreadsheets, email threads, shared drives, and legacy systems?
For many healthcare organizations, the answer is no. Compliance teams may know that policies exist, clinical leaders may know which AI tools are being used, IT may know where models are deployed, and legal teams may know which regulations apply. Yet there may be no single, continuously updated system that connects those facts into an enterprise-wide governance picture.
This is the business case behind AI healthcare governance software development.
A modern governance platform can create a centralized inventory of AI systems, map applications to regulations and internal policies, automate risk assessments, manage approvals, track model validation, monitor performance, maintain evidence, assign accountability, and generate audit-ready reports. For a hospital executive, the objective is not simply to "add AI." It is to create an operational control layer around AI adoption.
The market is moving quickly. Grand View Research estimates that the global AI in healthcare market will grow from $50.7 billion in 2026 to $505.6 billion by 2033, representing a 38.9% CAGR.
For a Chief Compliance Officer preparing a board proposal, the more important question is not whether healthcare AI will grow. It is whether the organization can govern that growth without multiplying compliance workload and operational risk.
This guide explains how to build scalable AI healthcare governance software for enterprise health systems, including architecture, governance modules, development stages, technology choices, realistic custom development costs, ROI calculations, and implementation challenges.
It also addresses the exact concern many hospital executives have: which organizations have demonstrated healthcare AI governance in practice, and which technology partners can credibly support such a platform? Public evidence is still limited for vendors claiming hospital-specific governance efficiency improvements. Therefore, this article separates independently documented healthcare governance outcomes from vendor-reported case studies rather than treating marketing claims as audited evidence.
For organizations evaluating AI healthcare compliance governance software development services or looking to develop AI powered healthcare governance software, that distinction is critical.

What if a hospital could see the governance status, risk level, compliance evidence, and performance of every AI system from one centralized platform instead of searching through spreadsheets, emails, and disconnected legacy applications?
That is the core purpose of AI healthcare governance software. It is an enterprise software platform designed to help hospitals and healthcare organizations discover, assess, approve, monitor, document, and control artificial intelligence throughout its entire lifecycle.
Unlike conventional compliance software, an AI healthcare governance platform is specifically designed for the risks created by AI systems, including clinical safety, patient privacy, cybersecurity, model performance, bias, regulatory compliance, vendor risk, and ongoing model changes.
The platform typically operates through a continuous governance lifecycle:
AI discovery → registration → risk assessment → compliance review → approval → deployment → monitoring → incident management → revalidation → retirement
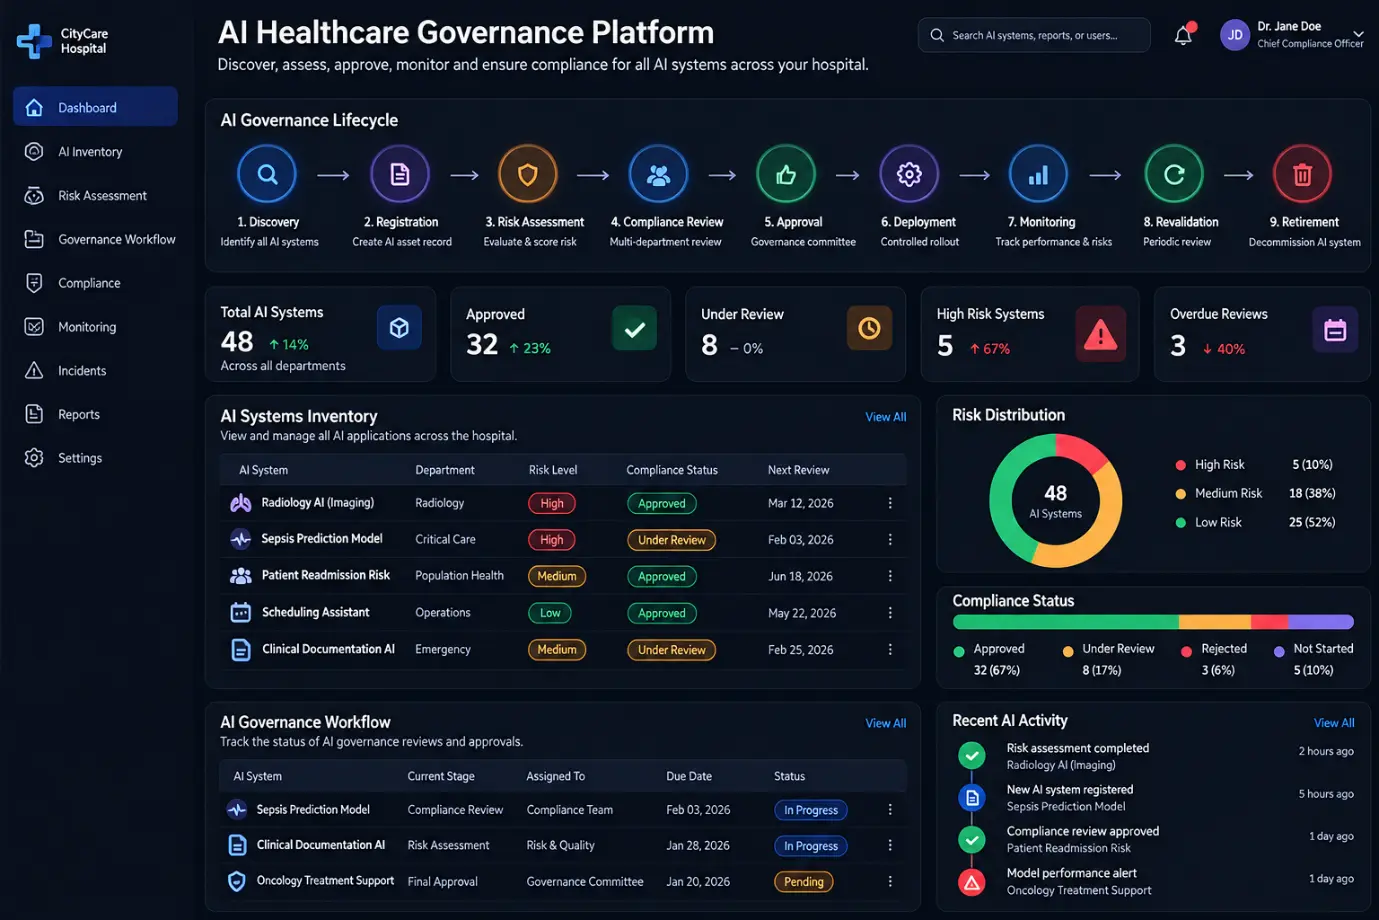
The software creates a centralized AI asset registry containing every approved, pending, and potentially unauthorized AI application across the healthcare organization.
Each AI asset can include information about its:
The platform evaluates each AI system against configurable risk criteria. A clinical diagnostic model, for example, may receive a higher risk classification than an administrative scheduling algorithm.
Risk scoring can consider patient safety, PHI exposure, clinical impact, cybersecurity, bias, explainability, automation level, and regulatory requirements.
After risk classification, the software routes the AI application through the appropriate approval workflow.
It can automatically assign tasks to:
This creates a documented chain of accountability.
Governance does not end when an AI application is approved.
The platform can monitor model performance, incidents, documentation, regulatory changes, review deadlines, and model versions. When a significant change occurs, the system can trigger reassessment or revalidation.
Finally, AI healthcare governance software development creates a centralized reporting layer where executives can view compliance status, high-risk AI systems, overdue reviews, incidents, control gaps, and governance KPIs.
For enterprise health systems, this converts AI governance from a periodic manual exercise into a continuous, evidence-based operational process. The result is greater visibility, faster governance decisions, stronger audit readiness, and a scalable foundation for responsible AI adoption.
An enterprise AI healthcare governance platform should do more than track AI models. It should connect regulatory compliance, policies, provider governance, patient safety, clinical quality, workforce competency, vendor oversight, and executive accountability in one controlled environment. This is especially important for health systems where governance information is currently distributed across spreadsheets, email threads, shared drives, and legacy applications.
For a hospital asking how to make AI healthcare governance software capable of supporting enterprise compliance, the following eight modules form the foundation.
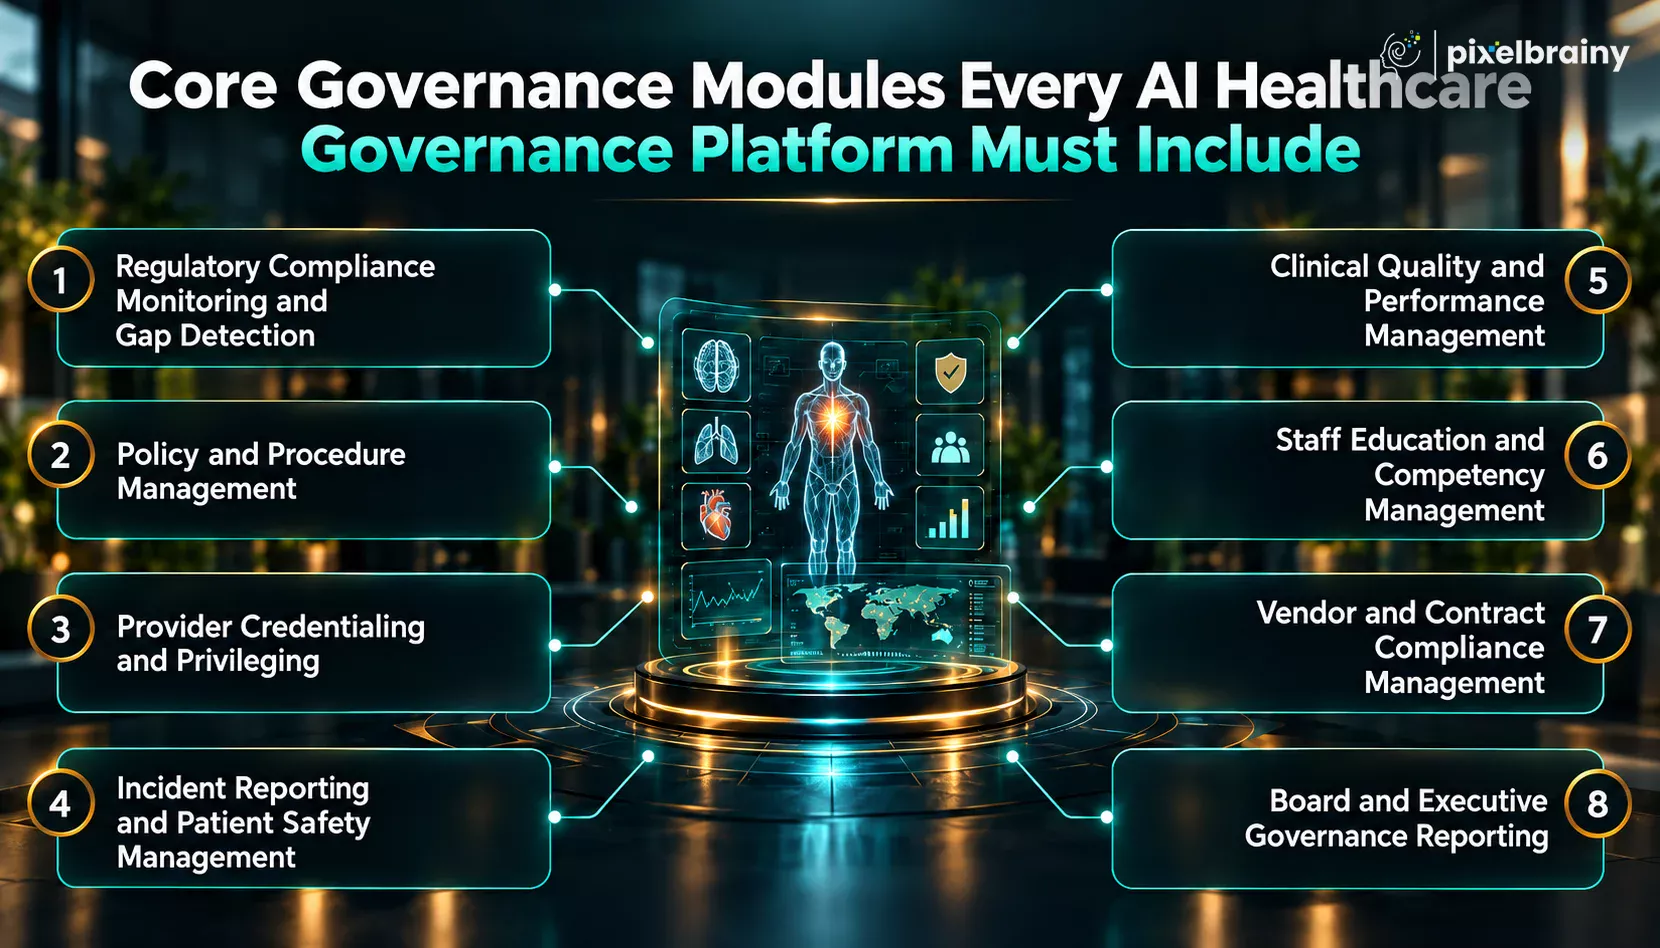
A healthcare governance platform should continuously map organizational controls against applicable requirements from CMS, The Joint Commission, OIG, federal regulations, and internal standards. This is increasingly important because requirements and accreditation structures change. For example, The Joint Commission introduced National Performance Goals for hospitals effective January 1, 2026, while its 2026 Survey Process Guide replaced the previous hospital Survey Activity Guide. The module should provide:
For the real query involving disconnected spreadsheets and email threads, this module creates a single source of truth for enterprise compliance status instead of requiring the Chief Compliance Officer to manually consolidate departmental updates.
Building AI healthcare governance software with policy management and workflow features requires more than storing PDF documents.
The platform should manage the complete policy lifecycle:
Draft → Review → Approval → Publication → Staff acknowledgment → Version control → Periodic review → Retirement
AI can help identify outdated policies, summarize regulatory changes, suggest affected documents, and connect policies to specific controls and departments.
OIG's healthcare compliance guidance specifically identifies written policies and procedures as a fundamental component of an effective compliance program.
This makes policy management a core capability when developing AI healthcare governance software with real-time compliance monitoring features.
For a health system managing 2,400 providers across eight hospitals, credentialing should be treated as an enterprise governance workflow rather than an administrative database.
To build AI healthcare governance software with credentialing and privileging management features, the platform should automate:
The system can flag an expired license, sanction event, missing credential, or privilege requirement and route it to the appropriate medical staff office.
The Joint Commission states that credentialing and privileging processes must evaluate practitioner qualifications and current competence, while continuing education and performance information can inform reappointment and privilege decisions.
To build AI healthcare governance software with clinical quality and patient safety features, incident management must be connected directly to governance.
The platform should capture:
Incident → Classification → Investigation → Root Cause Analysis → Corrective Action → Owner → Verification → Closure
AI can help categorize incidents, identify recurring patterns, summarize investigation evidence, and highlight potential systemic risks. Human clinical and compliance professionals should retain decision-making authority.
This creates a connection between individual incidents and enterprise patient-safety trends instead of keeping reports isolated within departments.
A governance platform should connect compliance with actual clinical performance.
Dashboards can monitor:
This is particularly important when AI is involved in clinical decision support. Governance should evaluate not only whether an AI system was approved, but whether it continues to perform safely in the real clinical environment.
Governance fails when employees do not understand the policies they are expected to follow.
The platform should connect policies and risks to employee education requirements.
Features can include:
This allows organizations to identify whether required education has actually reached the workforce.
Healthcare organizations increasingly depend on external AI vendors, technology providers, clinical service companies, and software platforms.
A governance platform should track:
This becomes especially important when an external AI vendor updates a model or changes how data is processed.
Finally, how to create AI healthcare governance software with board and executive reporting features comes down to turning operational data into decision-ready intelligence.
A board dashboard should answer:
The strongest AI healthcare governance software development architecture therefore connects every module to a common governance data layer:
Regulations → Policies → Providers → AI Systems → Incidents → Quality → Training → Vendors → Executives
This integrated approach is the foundation for AI healthcare governance software development services that can scale from one hospital to an enterprise health system. Instead of simply developing AI healthcare governance software as another compliance application, organizations can create a continuously updated governance infrastructure that gives compliance officers, clinical leaders, medical staff offices, executives, and boards a shared view of risk, accountability, and performance.
Why should a healthcare organization invest in AI governance software before its AI portfolio becomes too complex to control manually? The answer is increasingly tied to operational scale, regulatory pressure, fragmented accountability, and the speed at which healthcare organizations are adopting AI.
For a hospital or health system still managing compliance through spreadsheets, email threads, shared drives, and legacy applications, AI healthcare governance software development is not simply a technology upgrade. It is an infrastructure decision that determines whether AI oversight can scale alongside AI adoption.
The first reason to invest is straightforward: healthcare organizations are already deploying AI faster than many governance processes can mature.
The 2026 HIMSS Healthcare AI Trends Report, based on HIMSS research and Guidehouse analysis, found that 78% of health systems are currently engaged in AI projects, while only 52% consider themselves operationally ready to implement AI at scale.
That 26 percentage point gap is a governance warning.
For organizations evaluating how to develop an AI healthcare governance software, the investment question should therefore begin with operational readiness. If AI projects are expanding while governance remains dependent on manual processes, the organization needs infrastructure capable of managing that growth.
Healthcare organizations are no longer dealing with a small number of AI policies. Regulatory expectations are emerging across federal agencies, states, international frameworks, professional organizations, accreditation bodies, and voluntary standards.
A January 2026 analysis published in npj Digital Medicine identified 240 health AI policies in its Health & AI Policy Index snapshot. The analysis found that transparency and governance appeared in 60% of those policies, while safety and risk appeared in 48%. The researchers also reported a sharp increase in policy activity during 2024 and 2025.
This is a major reason for developing AI healthcare governance software with real-time compliance monitoring features.
A compliance team cannot efficiently monitor a growing regulatory landscape by manually searching websites, updating spreadsheets, and emailing department owners. A governance platform can create a structured relationship between:
Regulation → Requirement → Policy → Control → Evidence → Owner → AI System → Compliance Status
AI governance is increasingly becoming an executive accountability issue.
A board does not need a spreadsheet containing hundreds of compliance tasks. It needs an accurate answer to questions such as:
This is why organizations researching how to create AI healthcare governance software with board and executive reporting features should design executive reporting into the architecture from the beginning.
The purpose is not merely to produce attractive dashboards. The platform should convert operational governance data into structured decision information that supports executive oversight, risk committees, compliance committees, and board reporting.
Consider the real-world scenario of a health system managing credentialing and privileging for 2,400 providers across eight hospitals, while simultaneously managing AI applications, policies, clinical quality, incidents, vendors, and regulatory requirements.
At that scale, governance becomes a data coordination problem.
Provider credentials can change. Licenses expire. Vendors update software. AI models change versions. Policies are revised. Regulatory requirements evolve. Incidents create corrective actions. Clinical performance indicators move continuously.
The organization therefore needs a governance architecture capable of connecting these events rather than maintaining separate administrative databases.
This is a key reason to build AI healthcare governance software with credentialing and privileging management features when governance requirements extend beyond AI model inventories.
Another investment driver is accountability.
When governance information exists across spreadsheets, email conversations, shared folders, and departmental applications, it becomes difficult to establish a definitive record of:
Who approved what, under which policy, based on which evidence, and when?
An enterprise governance platform establishes a controlled system of record.
For every AI system, the organization can maintain:
This is central to the creation of AI healthcare governance software because governance requires traceability, not simply data storage.
Another reason to invest is the expanding scope of AI use.
AI governance may need to cover:
A governance platform therefore needs to operate as an enterprise control layer rather than as a narrow clinical AI registry.
Organizations considering AI healthcare governance software development services should evaluate whether the proposed architecture can govern both clinical and administrative AI while applying different risk tiers and approval workflows.
The 2026 healthcare environment shows a clear mismatch between AI adoption and organizational readiness. Deloitte's 2026 Global Health Care Outlook reports that approximately 30% of surveyed health systems are operating generative AI at scale in selected areas, while only 2% report AI deployment across their entire enterprise.
This indicates that healthcare AI is moving from isolated experimentation toward broader operational deployment, but enterprise-wide implementation remains immature.
For healthcare leaders, that creates a strategic reason to develop an AI healthcare governance software before AI becomes too deeply embedded across departments to manage through disconnected processes.
Healthcare businesses should invest in AI healthcare governance software when their current governance infrastructure cannot provide reliable visibility, accountability, regulatory mapping, workflow control, or evidence management at the scale of their AI operations.
The right question for executives is therefore not simply:
"Do we need another software platform?"
It is:
"Can our current governance infrastructure reliably control the AI systems, people, vendors, policies, clinical risks, and regulatory obligations we expect to manage over the next several years?"
For organizations where the answer is no, AI healthcare governance software development becomes an infrastructure investment for responsible AI scale, enterprise accountability, and regulatory readiness.
The objective is not to slow AI adoption. It is to build the governance capacity required to scale AI without losing control.
The decision to build AI healthcare governance software or buy a commercial platform should not start with the question, "Which option has more features?" It should start with a more practical question: How unique, complex, integrated, and strategically important is your organization's governance environment?
For some healthcare organizations, custom development is justified. For others, buying commercial software is clearly more economical. A third group will get the best result from a hybrid model.
Large health systems often operate across multiple hospitals, departments, states, EHR environments, and governance structures.
When governance workflows vary significantly between facilities, commercial platforms may require extensive customization. If the cost of continuous configuration, integrations, custom workflows, and vendor services begins approaching the cost of developing a dedicated platform, custom AI hospital governance software development may make more strategic sense.
Custom development becomes particularly compelling when the organization needs:
The objective is not to recreate commercial GRC software. It is to build an AI healthcare governance platform around the organization's actual operating model.
If a healthcare technology company intends to sell governance software to hospitals, developing the product internally can create a proprietary technology asset.
In this scenario, custom AI healthcare governance software development is not simply an internal IT expense. The software itself becomes the commercial product.
Ownership can provide control over:
This scenario is fundamentally different from a hospital deciding whether to build an internal governance platform.
Custom development can also make sense when governance requirements are highly specialized.
Examples include:
If a commercial platform cannot adequately represent these requirements without extensive workarounds, developing AI healthcare governance software around the organization's governance model may be preferable.
Private equity healthcare operators face a different challenge.
A portfolio may contain multiple hospitals, clinics, physician groups, and specialty providers using different EHRs and operating under different state regulations.
A centralized AI healthcare governance platform can provide portfolio-level visibility while allowing individual facilities to maintain local requirements.
Custom development may therefore be justified when portfolio governance itself is a strategic capability that commercial products cannot unify effectively.
A community hospital or critical access hospital with relatively standardized compliance requirements and limited internal engineering resources generally should not build a complex governance platform from scratch.
If an established commercial product already provides:
then licensing may provide better economics.
For these organizations, custom development can introduce unnecessary costs in engineering, cybersecurity, maintenance, upgrades, and regulatory validation.
If governance gaps are creating immediate regulatory or operational concerns, waiting 6 to 12 months for custom development may not be practical.
Commercial software can provide an established foundation much faster.
The organization can then improve governance immediately while evaluating whether future customization is justified.
If a hospital's requirements closely match an existing product, buying is usually the more rational choice.
Internal engineering resources may be better allocated toward:
In this situation, AI healthcare governance software development could consume resources without creating enough differentiated value.
The Hybrid Approach:
A hybrid strategy can be the most practical option for many enterprise healthcare organizations.
The organization can buy the standard governance infrastructure and build only the capabilities that provide meaningful differentiation.
For example:
Commercial platform: policy management, compliance workflows, audit management, standard risk controls
Custom modules: specialized regulatory monitoring, EHR integration, AI model governance, clinical data governance, and board-specific reporting.
This approach allows organizations to build AI healthcare governance software capabilities where customization matters without rebuilding commodity governance functionality.
Before choosing custom development, commercial licensing, or a hybrid approach, healthcare leaders should answer:
There is no universally correct answer. Build when governance complexity and strategic differentiation justify ownership, buy when requirements are standardized and speed matters, and choose hybrid when commercial infrastructure can handle the basics but your organization needs custom governance intelligence.
How can a multi-hospital health system make sure every AI application has a documented owner, risk classification, approval history, compliance evidence, vendor record, incident history, and scheduled review without forcing compliance teams to reconcile information from separate systems? This is one of the most important questions to answer before starting AI healthcare governance software development.
A healthcare organization planning to build AI healthcare governance software needs more than an AI inventory or compliance dashboard. The core platform should connect AI systems, regulatory requirements, policies, governance workflows, evidence, incidents, vendors, accountability, and executive reporting in one controlled environment.
The objective is to create a reliable governance foundation that can support clinical and administrative AI across departments and facilities. The features below represent the essential capabilities required for the initial platform. Advanced capabilities such as predictive governance analytics, autonomous AI agents, sophisticated model observability, and automated regulatory intelligence should be addressed separately.
| Core Feature | What It Should Do |
| AI System Inventory and Registry | A centralized registry should maintain every AI application's owner, vendor, purpose, department, model version, deployment environment, data sources, risk classification, approval status, and lifecycle stage. This creates the authoritative inventory required for enterprise AI governance and prevents important systems from remaining hidden inside departmental workflows. |
| AI Risk Assessment and Classification | The platform should evaluate each AI system against configurable factors such as clinical impact, patient safety, data sensitivity, affected populations, human oversight, and decision-making consequences. It should assign documented risk levels and preserve assessment history for governance review, escalation, and audit purposes. |
| Regulatory Compliance Management | Compliance teams should map applicable regulations, standards, accreditation requirements, and organizational obligations to AI systems and controls. The module should track requirements, responsible owners, evidence, deadlines, exceptions, and remediation activities without requiring teams to maintain separate spreadsheets or manually consolidate compliance information. |
| Compliance Gap Detection | The system should identify missing controls, incomplete documentation, overdue assessments, expired evidence, and unresolved compliance requirements. Each gap should connect automatically to responsible owners, remediation tasks, deadlines, escalation rules, and supporting evidence so compliance teams can manage deficiencies through a controlled workflow. |
| Policy and Procedure Management | Organizations should be able to create, review, approve, publish, version, acknowledge, periodically review, and retire governance policies from one controlled workspace. Policies should connect to applicable regulations, controls, departments, AI systems, and employee requirements, creating traceability throughout the policy lifecycle. |
| Governance Approval Workflows | Configurable workflows should route AI applications through appropriate compliance, privacy, legal, clinical, cybersecurity, quality, and governance reviewers. Approval paths should vary according to risk level and use case, while every decision, exception, reviewer, timestamp, and supporting document remains auditable. |
| Evidence and Document Management | The platform should provide a centralized repository for validation reports, vendor documentation, risk assessments, policies, approvals, contracts, security evidence, and compliance records. Versioning, document ownership, expiration dates, metadata, and audit history should eliminate uncontrolled files and repeated evidence collection. |
| AI Vendor Governance | Healthcare organizations should track third-party AI vendors, contractual obligations, security documentation, data-processing terms, risk assessments, model information, compliance evidence, renewals, and unresolved issues. Vendor records should connect directly with the AI systems, policies, controls, and risks associated with each supplier. |
| AI Incident Management | The platform should provide structured workflows for reporting, classifying, investigating, escalating, and closing AI-related incidents. Each incident should connect to the affected AI system, risk assessment, controls, investigation findings, corrective actions, responsible owners, and final resolution for complete governance traceability. |
| Corrective and Preventive Action Management | Governance teams need a structured mechanism for addressing identified compliance, safety, quality, and operational problems. The module should assign corrective actions, owners, deadlines, verification requirements, escalation rules, and closure evidence while maintaining the complete history for audits and management review. |
| Audit Trail and Accountability | Every material governance action should generate a tamper-evident record showing who performed the action, what changed, when it changed, and what information supported the decision. This creates defensible evidence for internal audits, regulatory reviews, investigations, and executive oversight. |
| Role-Based Access Control | Different users require different levels of governance access. The platform should support granular permissions for compliance officers, clinicians, AI owners, privacy teams, legal teams, administrators, executives, and board members while enforcing least-privilege access to sensitive healthcare and governance information. |
| Governance Task and Review Management | Recurring governance activities should become assigned tasks with deadlines, priorities, escalation rules, dependencies, and completion evidence. The system should identify upcoming reviews, overdue assessments, expiring documentation, and unresolved governance actions across departments, facilities, and responsible teams. |
| Executive Governance Dashboard | Executives should receive a consolidated view of AI inventory, risk distribution, compliance posture, open incidents, overdue actions, control status, and governance maturity. The dashboard should translate operational governance data into concise information suitable for executive committees, risk committees, compliance leadership, and board oversight. |
| Reporting and Audit Readiness | The platform should generate configurable compliance, governance, risk, incident, and AI portfolio reports using the same underlying evidence. This allows organizations to respond to auditors, regulators, governance committees, and executives without manually reconstructing information from disconnected spreadsheets, emails, and legacy applications. |
For organizations evaluating AI healthcare governance software development services, these capabilities should operate as one connected governance architecture rather than as separate software modules. A regulatory requirement should connect to a policy, the policy to controls, controls to evidence, and evidence to responsible owners. AI systems, vendors, incidents, corrective actions, and executive reporting should use the same underlying governance data model.
That connected architecture is what allows organizations to build AI healthcare governance software that can scale across hospitals, departments, clinical applications, and administrative AI use cases.
The right core feature set creates a dependable governance foundation, giving healthcare organizations one source of truth before advanced AI governance capabilities are added.
How can a large health system move beyond basic AI inventories and compliance workflows to continuously identify emerging AI risks, detect model changes, understand regulatory impact, and give governance leaders actionable intelligence before a problem reaches patients?
This is where advanced capabilities become valuable. Once the core governance foundation is established, organizations can build AI healthcare governance software with intelligent capabilities that continuously analyze governance data, identify patterns, prioritize risks, and support faster decision-making.
These features should not replace the core governance modules. Instead, they should sit on top of them and turn the platform from a system of record into a more proactive AI healthcare governance platform.
| Advanced Feature | What It Should Do |
| AI-Powered Regulatory Intelligence | An AI engine can continuously analyze approved regulatory and policy sources, identify potentially relevant changes, and map those changes to affected AI systems, policies, controls, and departments. Governance teams can then review suggested impacts instead of manually checking every regulatory source. |
| Predictive AI Risk Scoring | Advanced risk models can evaluate historical incidents, system characteristics, compliance gaps, clinical context, vendor information, and monitoring data to identify AI systems that may require additional governance attention. The score should remain explainable and support human review rather than making autonomous compliance decisions. |
| Automated Model Drift Detection | The platform can continuously compare current AI performance with established baselines and identify changes in accuracy, data distribution, output patterns, or clinical performance. Significant deviations can automatically trigger investigation, review, or model revalidation workflows. |
| AI Bias and Fairness Monitoring | Advanced governance software can evaluate model performance across relevant patient populations and identify potential disparities in outcomes or error rates. Governance teams can establish thresholds, review subgroup performance, document investigations, and connect findings to corrective actions or deployment decisions. |
| Generative AI Governance and Guardrails | Organizations using enterprise generative AI can establish controls for approved models, prompts, data access, PHI handling, output review, prohibited use cases, and human oversight. The platform can record usage policies and governance decisions while supporting controlled adoption of generative AI across departments. |
| AI Governance Copilot | A governance copilot can allow compliance and clinical leaders to ask questions using natural language, such as "Which high-risk AI systems have overdue reviews?" or "Which deployed systems are missing current validation evidence?" Responses should be grounded in organizational governance records and provide traceable supporting evidence. |
| Digital AI Governance Map | A visual governance graph can connect AI systems with vendors, departments, data sources, regulations, policies, controls, owners, incidents, and approvals. This allows governance teams to understand the downstream impact when an AI model, vendor, regulation, or policy changes. |
| Automated Compliance Evidence Mapping | AI can analyze approved governance documents and evidence to suggest relationships between regulatory requirements, controls, policies, and supporting records. Human reviewers can approve or reject these mappings, reducing repetitive evidence classification while maintaining accountable oversight. |
| AI Change Impact Analysis | When a model version, vendor, data source, workflow, policy, or regulatory requirement changes, the system can identify potentially affected governance records. It can then recommend which risk assessments, approvals, validations, policies, and stakeholders require review before the change proceeds. |
| Enterprise AI Risk Simulation and Scenario Analysis | Advanced platforms can model hypothetical governance scenarios, such as a vendor failure, regulatory change, model performance decline, cybersecurity event, or rapid AI deployment across multiple facilities. Leaders can use these simulations to understand exposure, identify control weaknesses, and prepare response strategies. |
These advanced capabilities strengthen AI healthcare governance software development by turning the core platform into a proactive intelligence layer that helps healthcare organizations identify emerging AI risks, assess governance impact, and support faster, better-informed decisions.
Developing an AI healthcare governance software requires more than building dashboards, compliance checklists, or an AI inventory. Healthcare governance touches clinical operations, regulatory requirements, provider credentialing, patient safety, organizational policies, vendor oversight, audit evidence, and executive accountability. That makes the development process of AI healthcare governance software highly dependent on workflow accuracy, security, interoperability, and user adoption.
For organizations researching the steps to develop AI healthcare governance software from idea to launch, the right approach is to begin with governance requirements and operational workflows, then progressively validate the technology before clinical deployment. This is especially important for large health systems.
A real-world requirement can look like this:
“We are a health system operating 18 hospitals and our biggest governance challenge is maintaining consistent policy adherence, credentialing currency, and regulatory compliance documentation across all facilities when each hospital has its own administrative culture and our central compliance team cannot manually monitor everything simultaneously. Which development companies have built AI healthcare governance platforms for multi-facility health systems with centralized compliance visibility and facility-level workflow management at our scale?”
The answer requires a structured approach that connects enterprise requirements with facility-level workflows while maintaining centralized governance visibility.
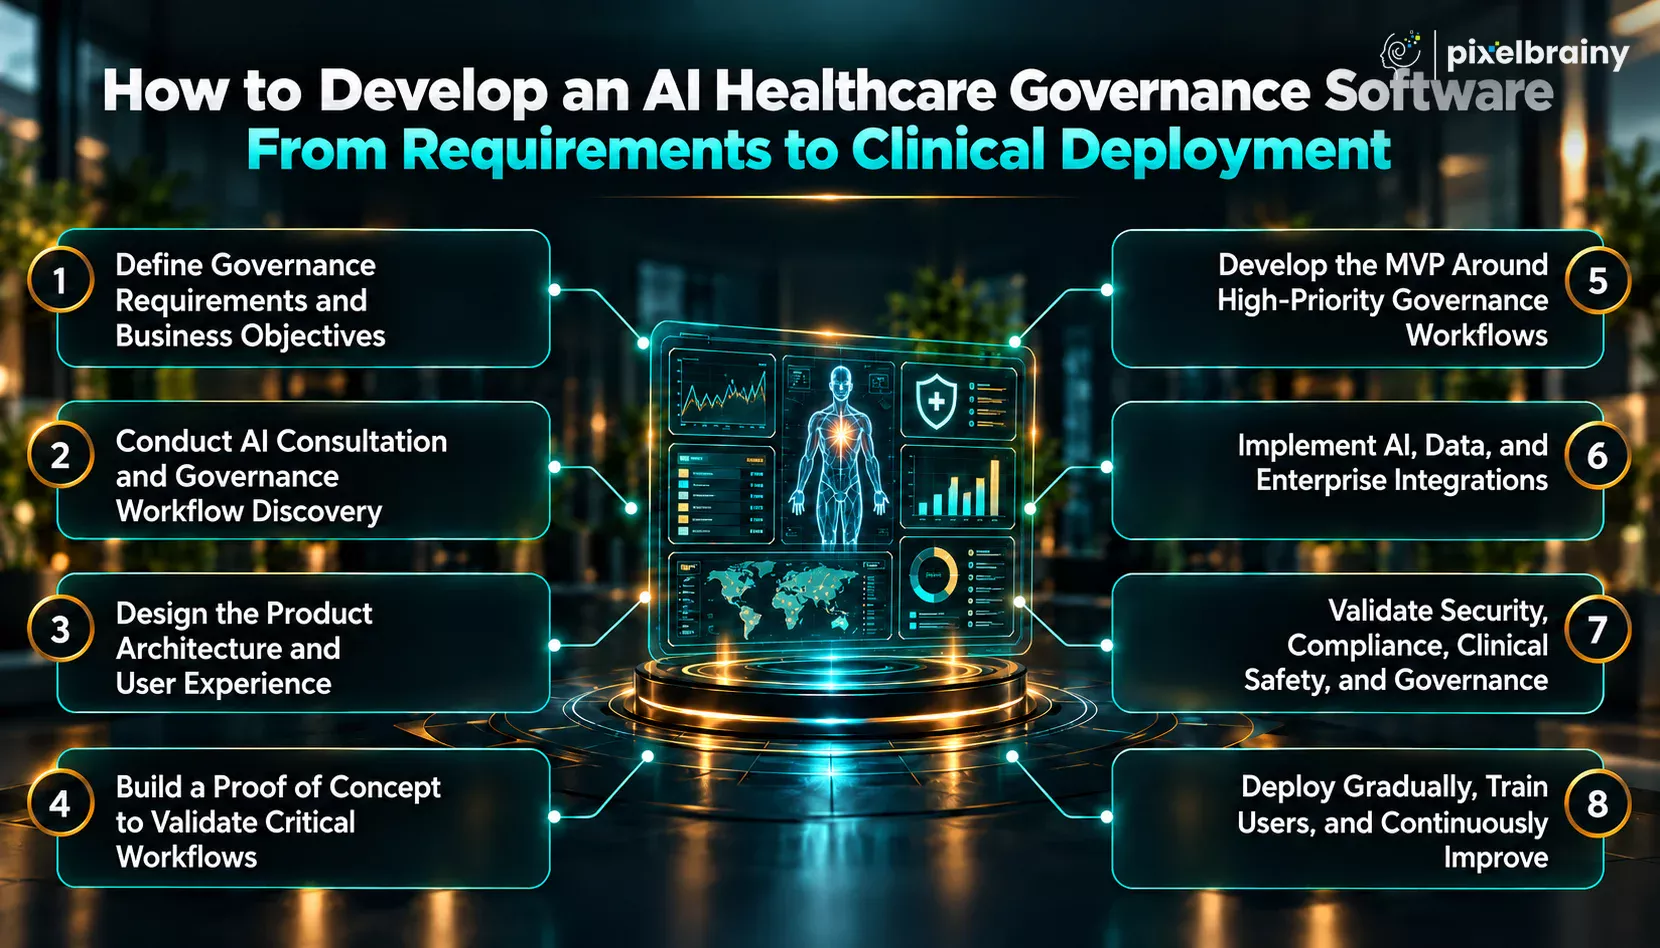
The first step in how to build AI healthcare governance software from scratch is identifying exactly what governance problems the platform must solve. Start by documenting current workflows for regulatory compliance, policy management, provider credentialing, incident reporting, quality management, AI oversight, vendor compliance, audits, and executive reporting.
Map which teams own each process, where information currently resides, what approvals are required, and where delays or compliance gaps occur. For multi-hospital organizations, document both enterprise-wide requirements and facility-specific variations.
Define measurable objectives such as reducing manual compliance tracking, improving audit readiness, accelerating approvals, increasing policy adherence, and creating centralized visibility.
This requirements foundation determines the product scope and prevents building an AI healthcare governance software around features that do not address real operational needs.
Once requirements are documented, organizations should validate the proposed architecture, workflows, AI use cases, regulatory considerations, and integration requirements through structured AI consultation.
The discovery process should involve compliance officers, clinical leaders, legal teams, medical staff offices, IT security teams, quality departments, risk managers, and executive stakeholders. Their input helps identify differences between documented policies and actual operational practices.
At this stage, teams should prioritize use cases according to business value, implementation complexity, regulatory sensitivity, and data availability. For example, automated compliance evidence collection may be suitable for an early release, while predictive risk scoring may require significantly more validation.
This step creates a practical blueprint for developing an AI healthcare governance software that reflects how healthcare organizations actually operate rather than how governance processes appear on paper.
Also Read: Top 10 AI Consulting Companies in USA
After defining requirements, establish the technical architecture, information structure, user roles, workflows, security model, and integration framework. The platform should support centralized governance while allowing individual hospitals, departments, and administrators to manage their assigned responsibilities.
The user experience should be designed around the needs of different stakeholders. Compliance teams may require evidence and regulatory dashboards, while clinical leaders need risk and quality information. Executives may need high-level governance indicators, whereas facility administrators need task-based workflows.
A specialized UI/UX design company can help translate complex governance processes into intuitive interfaces without hiding important compliance information.
The architecture should also anticipate future modules, additional facilities, new regulations, evolving AI models, and increasing governance data volumes.
Before committing to full-scale development, create a PoC development phase around the highest-risk or highest-value workflows. The objective is not to build the complete platform but to prove that critical technical and operational assumptions work.
A healthcare organization might validate centralized policy management, automated compliance evidence collection, AI inventory registration, credential expiration monitoring, or facility-level approval workflows.
The proof of concept should test data availability, integration feasibility, workflow logic, security controls, user permissions, and expected automation accuracy.
This stage is particularly valuable for large health systems because it can reveal differences between hospitals before substantial development investment is made. Successful validation provides evidence for moving toward MVP development, while failed assumptions can be corrected before they become expensive architectural problems.
The MVP should contain the minimum set of capabilities required to solve a clearly defined governance problem and demonstrate measurable value. Instead of attempting to automate every governance function immediately, prioritize essential capabilities such as AI asset registration, risk classification, policy management, compliance workflows, evidence management, incident tracking, audit trails, and governance reporting.
During MVP development, establish clear acceptance criteria for every workflow and validate them with representative healthcare users.
The MVP should also include essential security capabilities such as role-based access, authentication, authorization, encryption, audit logging, and appropriate data segregation.
A focused MVP allows the organization to test adoption, workflow efficiency, system performance, and governance outcomes before expanding into more complex capabilities.
Also Read: Top 10 AI MVP Development Companies in USA
Once the core platform is validated, integrate the systems required to make governance information useful and current. AI integration may connect governance workflows with EHR environments, credentialing systems, HR platforms, learning management systems, quality systems, contract repositories, identity platforms, document management systems, and enterprise analytics.
AI capabilities can support document classification, regulatory intelligence, risk analysis, evidence mapping, anomaly detection, and governance recommendations. However, automation should remain explainable and subject to appropriate human review.
If proprietary models or specialized prediction capabilities are required, AI model development should include data validation, performance testing, bias assessment, monitoring, and model governance.
Integration architecture should use secure APIs and standardized data structures wherever possible to support future expansion across facilities.
Also Read: Top 12+ AI Model Development Companies in the USA
Before clinical deployment, the software must undergo rigorous validation. This includes security testing, privacy assessment, access-control verification, audit-log validation, integration testing, workflow testing, performance testing, and disaster-recovery evaluation.
Healthcare organizations should also validate whether automated recommendations or AI-generated outputs could influence clinical, credentialing, compliance, or patient-safety decisions. Human oversight must be clearly defined for high-impact workflows.
Independent testing and governance review can help identify vulnerabilities and operational risks that internal development teams may overlook. Organizations evaluating AI development companies should therefore examine their experience with healthcare security, regulatory workflows, interoperability, validation, and production deployment rather than evaluating technical skills alone.
The platform should not enter production simply because the software works technically. It should be demonstrably safe, secure, auditable, and operationally appropriate.
The final stage of to create AI healthcare governance software successfully is controlled clinical and enterprise deployment. Start with a pilot facility or selected governance workflows before expanding across the organization.
Provide role-specific training for compliance officers, administrators, clinical leaders, credentialing teams, quality professionals, IT teams, and executives. Establish support procedures, escalation paths, governance ownership, and performance monitoring before wider rollout.
After launch, monitor adoption, workflow completion, compliance gaps, false alerts, user feedback, integration performance, and AI output quality. Use these findings to improve the platform continuously.
Organizations may hire AI developers with healthcare experience for ongoing product evolution or work with specialized development partners when internal teams need additional expertise. The objective is to treat deployment as the beginning of continuous governance improvement, not the end of development.
A disciplined development process helps healthcare organizations move from governance requirements to a secure, scalable, and clinically deployable AI governance platform with measurable operational value.
Also Read: A Guide to Proof of Concept (PoC) Development for AI Clinical Workflow System
The cost to develop an AI healthcare governance software generally ranges from $50,000 to $300,000+, depending on features, AI capabilities, healthcare integrations, security requirements, and deployment scale. A basic platform may require around $50,000 to $100,000, while advanced and enterprise platforms can reach $200,000 to $300,000 or more.
The development budget of AI healthcare governance software should be based on actual requirements rather than feature count alone. For accurate cost estimation of AI healthcare governance software development, healthcare businesses should consider regulatory workflows, EHR integration, AI intelligence, data security, multi-facility support, testing, and long-term maintenance.
A real-world cost question is:
“I am comparing three development proposals for AI healthcare governance software for our hospital network and the quotes range from $100,000 to $250,000 for similar stated core features. What legitimately drives this price variation and what specific questions about HIPAA architecture, healthcare regulatory content accuracy, EHR integration depth, and Joint Commission workflow alignment should I ask each vendor to evaluate whether their proposed software delivers genuine AI governance intelligence or a basic document management system with an AI label?”
This highlights why AI healthcare governance software development cost for healthcare businesses can vary significantly even when vendors appear to offer similar functionality.
| Software Type | Estimated Cost | Typical Scope |
| Basic AI Healthcare Governance Software | $50,000 to $100,000 | AI inventory, risk classification, policy management, compliance workflows, evidence management, user roles, audit trails, notifications, and basic reporting. |
| Advanced AI Healthcare Governance Software | $100,000 to $200,000 | Advanced risk assessment, regulatory intelligence, compliance mapping, incident management, vendor governance, credentialing workflows, analytics, APIs, automation, and enhanced security. |
| Enterprise AI Healthcare Governance Software | $200,000 to $300,000+ | Multi-hospital governance, EHR integrations, advanced AI risk intelligence, predictive analytics, model monitoring, regulatory intelligence, complex permissions, enterprise security, scalable infrastructure, and deployment support. |
| Cost Factor | Estimated Cost | Impact on Development |
| Requirements Discovery | $5,000 to $15,000 | Maps compliance, clinical, credentialing, risk, and executive workflows before development. |
| HIPAA-Compliant Architecture | $10,000 to $30,000+ | Covers encryption, access control, audit logging, data protection, secure infrastructure, and privacy requirements. |
| EHR Integration | $15,000 to $60,000+ per integration | Cost depends on API complexity, data exchange, workflow depth, and whether integration is one-way or bidirectional. |
| Regulatory Content and Rules Engine | $10,000 to $40,000+ | Covers regulatory mapping, compliance rules, evidence relationships, versioning, and regulatory updates. |
| Joint Commission Workflow Alignment | $10,000 to $30,000+ | Adds accreditation workflows, evidence tracking, corrective actions, ownership, and facility-level accountability. |
| AI Risk Assessment | $10,000 to $35,000+ | Includes automated classification, risk scoring, configurable rules, explanations, and human review workflows. |
| AI Regulatory Intelligence | $20,000 to $60,000+ | Covers regulatory document analysis, change detection, semantic processing, source validation, and alerts. |
| AI Model Development | $20,000 to $75,000+ | Includes data preparation, model development, evaluation, monitoring, and performance management. |
| Advanced Analytics | $10,000 to $30,000+ | Adds executive dashboards, risk trends, facility comparisons, analytics, and detailed reporting. |
| Multi-Hospital Architecture | $20,000 to $60,000+ | Supports centralized governance with facility-specific workflows, permissions, configurations, and reporting. |
| Security and Compliance Testing | $10,000 to $30,000+ | Includes security testing, vulnerability assessment, access validation, audit testing, and remediation. |
| Cloud Infrastructure and DevOps | $10,000 to $35,000+ | Covers production environments, monitoring, backups, disaster recovery, deployment, and scalability. |
| UX and Workflow Design | $8,000 to $25,000+ | Designs role-specific dashboards, approval workflows, alerts, and governance interfaces. |
| Data Migration | $10,000 to $40,000+ | Covers migration and cleansing of policies, compliance records, provider data, documents, and legacy governance information. |
| Testing and QA | $10,000 to $35,000+ | Includes functional, integration, security, performance, regression, and user acceptance testing. |
| Training and Deployment | $5,000 to $20,000+ | Covers user training, configuration, documentation, rollout, and implementation support. |
| Annual Maintenance | 15% to 25% of development cost | Covers security updates, regulatory changes, integrations, infrastructure, AI monitoring, fixes, and ongoing improvements. |
The development pricing of AI healthcare governance software depends mainly on healthcare complexity, AI capabilities, integrations, security, and deployment scale. A realistic budget should account for both initial development and ongoing regulatory, technical, and AI maintenance requirements.
For healthcare CFOs, CMOs, and CCOs, the ROI of AI healthcare governance software should be measured in financial terms, not generic efficiency claims. The strongest business case comes from five areas: avoiding regulatory risk, reducing credentialing labor, lowering policy management costs, reallocating compliance staff capacity, and reducing emergency survey preparation.
For organizations evaluating whether to build AI healthcare governance software or buy an existing platform, these categories provide a practical framework for presenting the investment to finance leadership and the board.
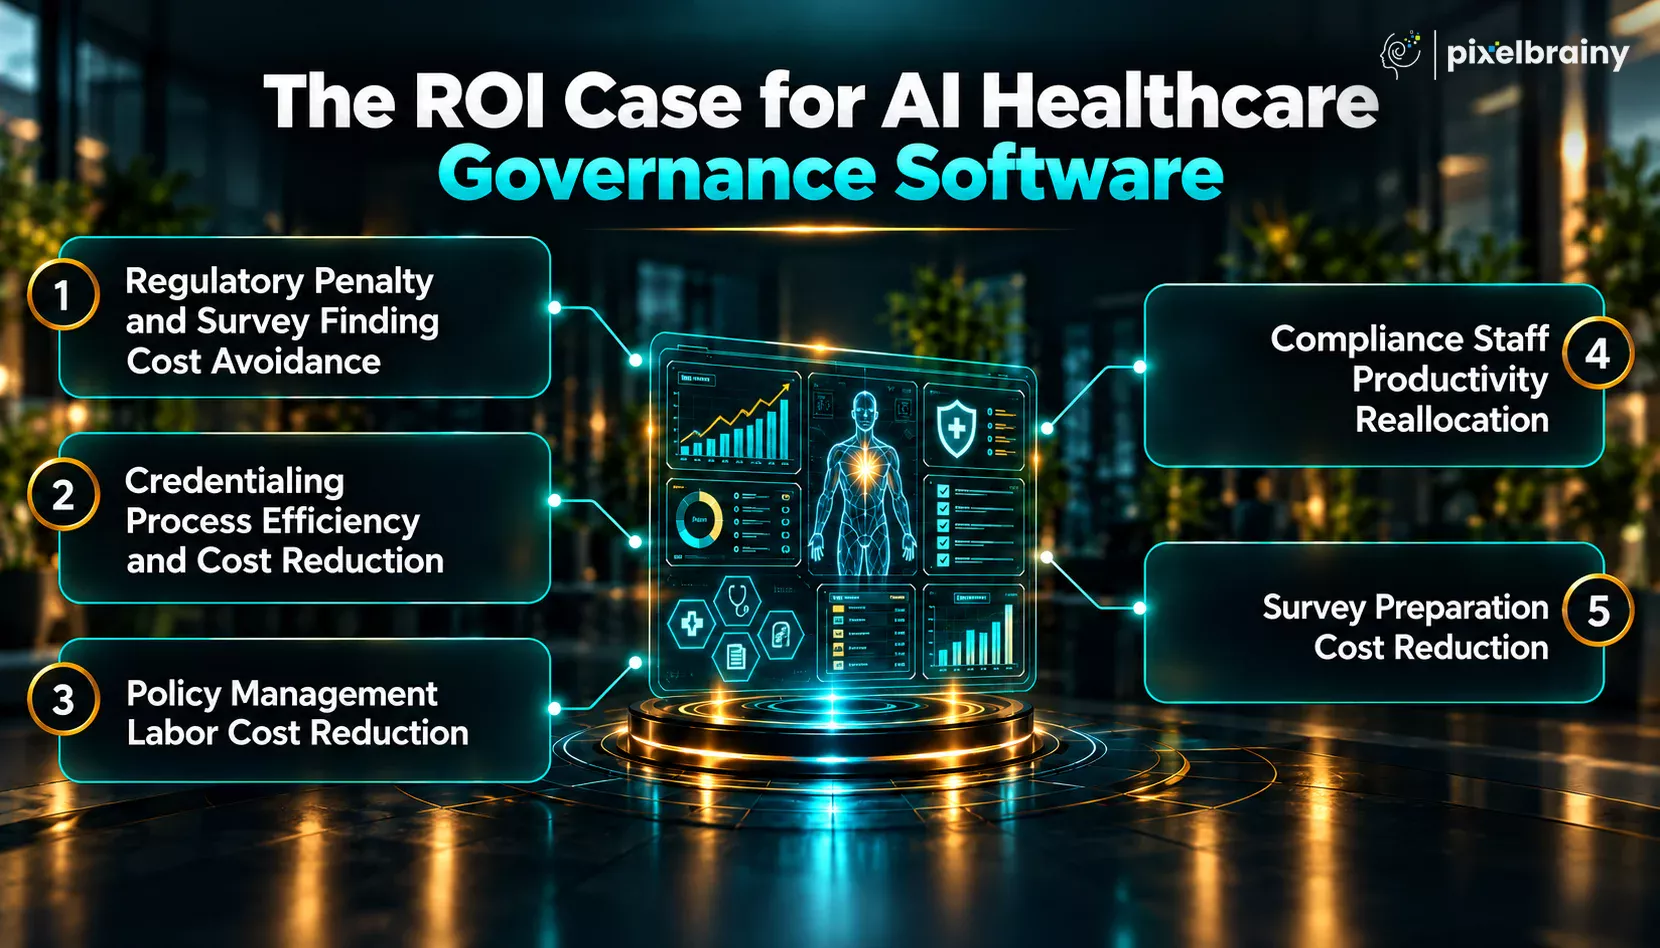
Continuous governance monitoring can identify missing evidence, overdue corrective actions, outdated policies, and compliance gaps before they become survey findings or enforcement issues.
There is no standard dollar value for a Joint Commission finding, so a realistic ROI model should treat $15,000 to $50,000+ per significant finding as an illustrative planning assumption covering remediation work, consultant support, leadership time, documentation, and operational disruption.
CMS enforcement can create much larger exposure when serious deficiencies affect Medicare participation. OIG investigations can also result in settlements and Corporate Integrity Agreements that require additional compliance resources, independent reviews, reporting, training, and monitoring for five years.
Illustrative annual value: $50,000 to $150,000+
Credentialing teams spend substantial time on primary-source verification, document collection, license checks, expiration tracking, and recurring provider monitoring. Automation can reduce repetitive administrative work while improving visibility into credential status.
As of October 2026, Salary.com reports an average U.S. hospital credentialing specialist salary of $92,590 per year, or approximately $45 per hour.
For example, if automation saves 4 hours across 600 credentialing activities annually, that represents about $108,000 in staff capacity. Additional financial value can come from reducing provider onboarding delays, although lost clinical revenue varies considerably by specialty and should be calculated separately.
Illustrative annual value: $75,000 to $150,000
Hospitals often maintain hundreds or thousands of policies across clinical, administrative, quality, HR, compliance, and operational departments. Manual review requires policy owners and compliance teams to identify regulatory changes, compare documents, collect approvals, and maintain evidence.
For a hospital with 1,000 policies, even 30 minutes of administrative coordination per policy represents 500 hours annually. AI-assisted policy comparison, regulatory alignment, version control, expiration alerts, and workflow routing can reduce this administrative workload.
Illustrative annual value: $25,000 to $60,000
Compliance professionals frequently spend valuable time assembling evidence, preparing reports, reconciling spreadsheets, tracking corrective actions, and responding to documentation requests.
AI automation can redirect that capacity toward proactive compliance monitoring, investigations, education, risk assessment, and remediation.
For example, reallocating 20% of the workload of four compliance professionals with a fully loaded annual cost of $120,000 each represents approximately $96,000 of productive capacity. The objective is not necessarily headcount reduction. It can instead help an existing team manage a larger governance workload without immediately adding staff.
Illustrative annual value: $75,000 to $125,000
Continuous governance monitoring can reduce the expensive cycle of discovering compliance gaps shortly before a regulatory survey. Instead of assembling evidence manually under deadline pressure, teams can maintain documentation, ownership, corrective actions, and compliance status throughout the year.
For a 300-bed hospital, an illustrative planning range of $50,000 to $150,000 can be used for intensive survey preparation involving staff time, overtime, consultants, documentation work, and operational disruption. A 30% reduction in emergency preparation effort could represent $15,000 to $45,000 annually.
Illustrative annual value: $15,000 to $45,000
| ROI Category | Illustrative Annual Value |
| Regulatory risk and finding avoidance | $100,000 |
| Credentialing efficiency | $100,000 |
| Policy management labor savings | $40,000 |
| Compliance productivity | $90,000 |
| Survey preparation reduction | $30,000 |
| Estimated annual value | $360,000 |
| 3-year gross value | $1.08 million |
If the hospital invests $250,000 in software development or implementation, the illustrative three-year net value would be $830,000.
3-Year ROI = ($1.08M − $250K) ÷ $250K × 100 = 332%
This framework can also be adapted for AI healthcare compliance governance software development, AI healthcare data governance software development, PE-owned healthcare portfolios, and FQHC networks by changing provider volume, facility count, compliance staffing, integration requirements, and regulatory exposure.
ROI varies significantly by organization size, governance maturity, and regulatory risk profile, with the strongest returns generally occurring where the gap between current governance capability and required compliance standards is greatest.
A reliable AI healthcare governance software requires a technology stack that can securely manage healthcare data, regulatory information, AI models, governance workflows, integrations, and audit evidence. The technology decisions directly influence scalability, security, development cost, interoperability, and long-term maintenance.
For teams researching the technology stack for AI healthcare governance software development, the architecture should support HIPAA-conscious data handling, role-based access, healthcare interoperability, AI-assisted risk analysis, regulatory intelligence, workflow automation, and enterprise reporting. The stack should also make it practical to develop AI healthcare governance software that can expand from one hospital to a multi-facility health system.
A common buyer question is:
“We want to build an AI healthcare governance platform that connects with our EHR, compliance systems, credentialing data, policy repository, and enterprise identity platform. Which technologies should we use for secure healthcare data integration, AI governance workflows, regulatory intelligence, audit trails, and scalable deployment across multiple hospitals?”
The answer is not a single programming language or AI model. A production-ready platform requires multiple technology layers working together.
| Technology Layer | Recommended Technologies | Role in the Platform |
| Frontend | React.js, Next.js, TypeScript | Builds responsive governance dashboards, compliance workflows, AI risk views, approval screens, reporting interfaces, and role-specific experiences. |
| Backend | Python, FastAPI, Node.js | Handles business logic, governance workflows, APIs, automation, authentication services, AI orchestration, and communication between platform components. |
| Primary Database | PostgreSQL | Stores users, governance records, policies, risk assessments, workflows, approvals, compliance activities, and structured healthcare governance data. |
| Document Storage | Amazon S3, Azure Blob Storage, Google Cloud Storage | Securely stores policies, audit evidence, regulatory documents, credentialing records, reports, and supporting governance documentation. |
| AI and Machine Learning | Python, PyTorch, TensorFlow, scikit-learn | Supports risk scoring, classification, anomaly detection, predictive analytics, document analysis, and specialized AI governance models. |
| Generative AI and LLM Layer | OpenAI models, Azure OpenAI, Anthropic, open-source LLMs | Enables regulatory document analysis, governance assistants, policy comparison, natural-language search, summarization, and compliance intelligence. |
| Vector Database | pgvector, Pinecone, Weaviate | Enables semantic search across policies, regulations, governance documents, audit evidence, and other unstructured information. |
| Healthcare Interoperability | HL7, FHIR, SMART on FHIR | Supports secure exchange of healthcare information and integration with EHR and clinical systems. |
| API Integration | REST APIs, GraphQL, API Gateway | Connects the governance platform with EHRs, credentialing platforms, HR systems, learning platforms, contract systems, and enterprise applications. |
| Workflow Automation | Temporal, Camunda, or custom workflow engines | Automates approvals, compliance tasks, policy reviews, corrective actions, escalations, notifications, and recurring governance activities. |
| Identity and Access Management | OAuth 2.0, OpenID Connect, SAML, Auth0, Microsoft Entra ID | Provides authentication, single sign-on, role-based access, and controlled access to sensitive governance information. |
| Security | TLS, AES-256 encryption, secrets management, WAF, SIEM | Protects sensitive healthcare information and supports security monitoring, access control, threat detection, and secure communication. |
| Audit Logging | CloudWatch, Azure Monitor, ELK Stack, OpenSearch | Records user activity, governance decisions, system events, approvals, changes, and access history for accountability and audit readiness. |
| Cloud Infrastructure | AWS, Microsoft Azure, Google Cloud | Provides scalable infrastructure, databases, storage, networking, monitoring, backup, disaster recovery, and enterprise deployment capabilities. |
| DevOps and CI/CD | Docker, Kubernetes, GitHub Actions, GitLab CI/CD | Supports repeatable deployments, automated testing, containerization, infrastructure management, and controlled software releases. |
| Analytics and Reporting | Power BI, Tableau, Looker, custom dashboards | Provides executive governance reporting, facility comparisons, compliance trends, risk analysis, and operational performance insights. |
| Monitoring and Observability | Datadog, Prometheus, Grafana, OpenTelemetry | Monitors application performance, infrastructure health, integrations, AI services, errors, and system availability. |
| Testing | PyTest, Jest, Playwright, Postman | Supports unit, API, integration, workflow, regression, and end-to-end testing before production deployment. |
The right technology stack gives AI healthcare governance software the security, interoperability, AI intelligence, scalability, and auditability required for reliable healthcare deployment.
The AI healthcare governance software development process is more complex than building a standard enterprise compliance application because it must bring together healthcare data, regulatory requirements, AI systems, clinical workflows, security controls, and organizational accountability. A platform may work technically but still fail if its regulatory logic is inaccurate, its EHR integration is weak, or users cannot trust its recommendations.
For organizations planning to develop AI healthcare governance software, the biggest challenges usually appear around data, interoperability, AI reliability, regulatory change, security, and user adoption. These challenges should be addressed during architecture and product planning rather than after deployment.
A real-world requirement may sound like this:
“Our health system has multiple hospitals, different EHR workflows, hundreds of AI applications, and separate compliance teams. How can we develop one AI healthcare governance platform that provides centralized risk visibility while still respecting facility-level workflows, regulatory requirements, and clinical accountability?”
This is why successful AI healthcare governance software development requires healthcare-specific architecture and governance from the beginning.
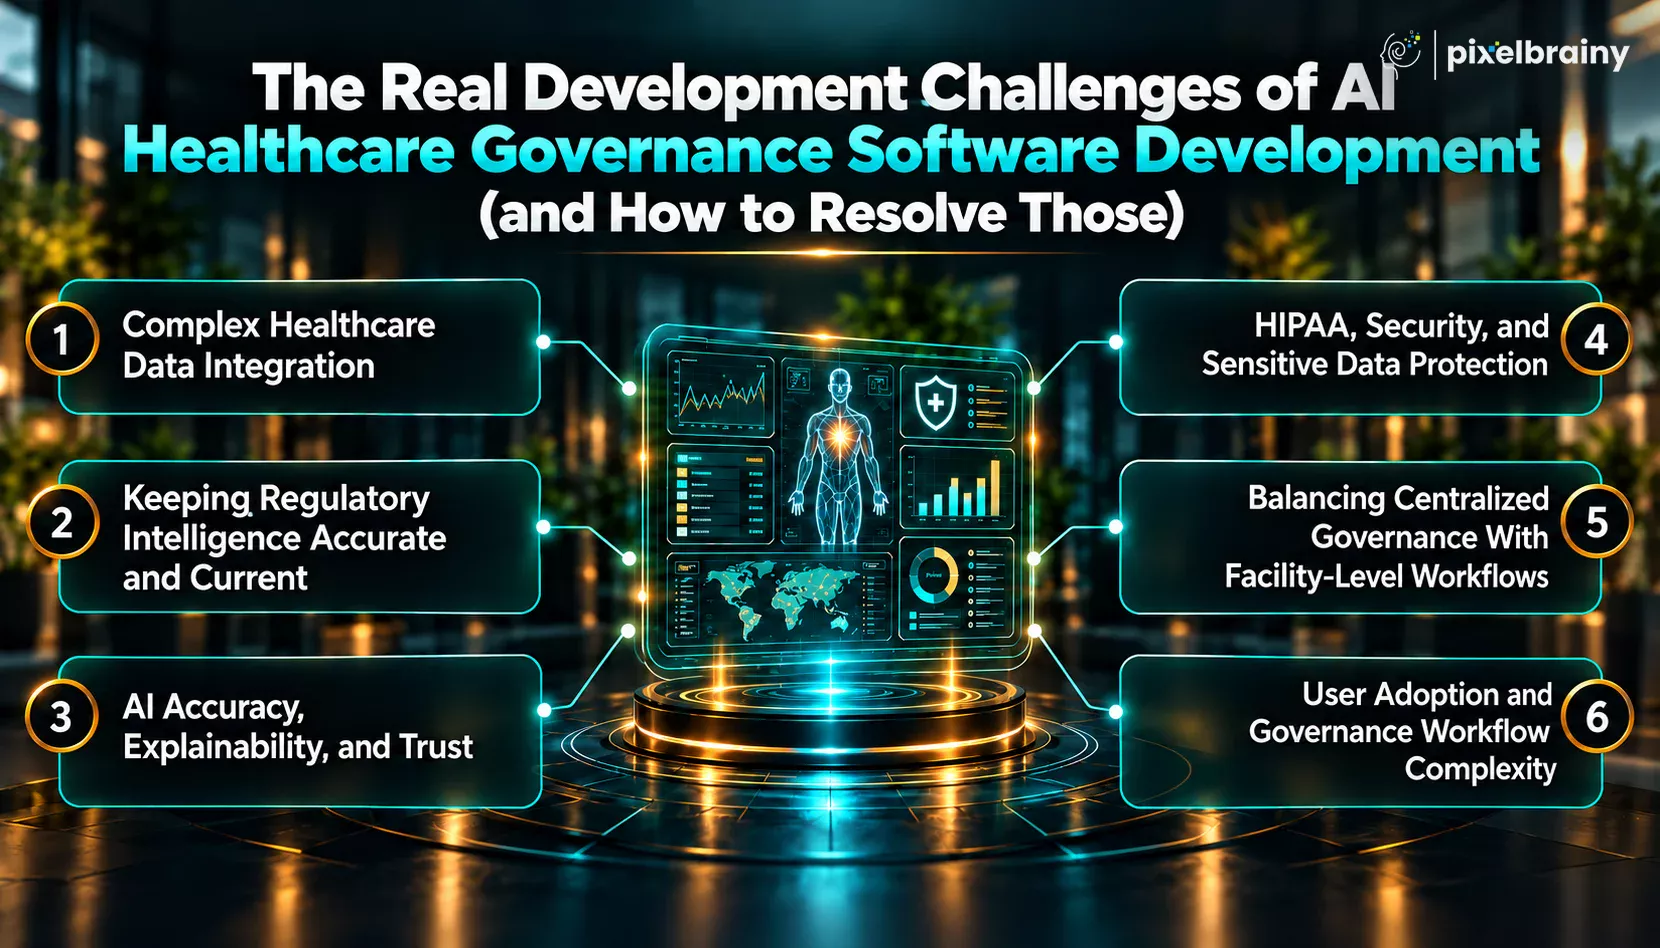
Healthcare governance information is usually distributed across EHRs, credentialing systems, policy repositories, HR platforms, quality systems, contract databases, spreadsheets, and legacy applications. Connecting these sources without creating duplicate or inconsistent information is one of the biggest development challenges.
Healthcare interoperability continues to evolve around standards such as FHIR, while ONC's 2026 interoperability guidance continues to emphasize standards-based exchange.
How to resolve it:
Use API-first architecture with FHIR and HL7 where appropriate, establish a centralized governance data model, and create clear ownership for every data source. Start with the highest-value integrations instead of attempting to connect every system simultaneously.
Healthcare regulations, accreditation requirements, organizational policies, and AI-related guidance can change over time. A governance platform that provides outdated regulatory information can create false confidence instead of reducing risk.
The challenge becomes greater when AI is used to interpret regulations because generated outputs must be traceable to authoritative sources and reviewed appropriately.
How to resolve it:
Build a regulatory knowledge layer that stores source documents, effective dates, versions, citations, mappings, and approval history. AI should identify potential changes and relationships, while qualified compliance professionals retain control over final interpretation and approval.
An AI governance platform may generate risk scores, identify compliance gaps, summarize policies, or recommend actions. However, healthcare organizations cannot treat AI output as automatically correct.
HHS continues to emphasize AI governance principles involving transparency, fairness, accountability, security, and privacy. Its 2026 OIG work plan also includes an audit of HHS AI governance.
How to resolve it:
Use explainable outputs, confidence indicators, source citations, human approval workflows, model evaluation, monitoring, and complete audit trails. High-impact recommendations should require appropriate human review before becoming governance decisions.
AI governance platforms may process sensitive provider, employee, operational, and potentially patient information. This creates significant requirements around authentication, authorization, encryption, audit logging, data retention, access management, and third-party AI services.
HHS has specifically highlighted the need to address privacy and security considerations when healthcare data and PHI are used with AI systems.
How to resolve it:
Design security into the architecture rather than adding it later. Apply least-privilege access, encryption, secure APIs, strong identity management, tenant and facility-level controls, continuous monitoring, vulnerability testing, and documented data-handling policies.
Large health systems often want one centralized governance platform but do not operate as one identical organization. Hospitals may have different policies, approval structures, clinical specialties, administrators, and compliance responsibilities.
A system that forces every facility into the same workflow can create resistance, while completely independent configurations can destroy enterprise visibility.
How to resolve it:
Use a configurable multi-facility architecture. Maintain centralized standards, reporting, risk visibility, and regulatory mappings while allowing authorized facilities to configure appropriate workflows, responsibilities, deadlines, and escalation paths.
Even technically advanced software can fail when compliance teams, clinicians, administrators, and executives find it difficult to use. Governance platforms involve many stakeholders, making workflow simplicity particularly important.
Users should not need to understand the underlying AI architecture to complete a compliance task or review a risk alert.
How to resolve it:
Design role-specific dashboards and workflows, automate repetitive tasks, minimize unnecessary data entry, provide clear explanations for AI-generated recommendations, and introduce the platform through controlled pilots. Measure adoption, task completion, false alerts, and user feedback after deployment.
The strongest AI healthcare governance platforms address these six challenges during development, creating a solution that is secure, interoperable, explainable, regulatory-aware, and practical for real healthcare operations.
From this above discussion, it is now time to identify the right development partner for a platform where healthcare compliance, AI intelligence, security, and operational workflows must work together. PixelBrainy as a leading AI healthcare software development company approaches governance platforms as enterprise healthcare products rather than basic compliance dashboards.
A question healthcare decision-makers often ask is:
“Which development companies have delivered AI governance software for hospitals with documented compliance efficiency improvement?”
The answer should not be based only on a vendor's AI feature list. Healthcare organizations should evaluate experience with regulated workflows, healthcare data, EHR integration, security, AI implementation, usability, and measurable operational outcomes.
PixelBrainy's AI healthcare governance software development services follow a structured approach that starts with understanding the organization's governance model, regulatory requirements, users, existing systems, and operational gaps.
The approach typically includes:
Organizations looking to build AI healthcare governance software can also start with a focused proof of concept or MVP before expanding into a broader enterprise platform. This approach helps validate workflows, AI accuracy, user adoption, and integration requirements before significant scale-up.
In one confidential U.S. healthcare project, PixelBrainy worked with a healthcare provider to develop an AI-enabled clinical workflow solution focused on documentation and care coordination. The platform processed structured and unstructured healthcare information, integrated with existing EHR workflows, and introduced AI-assisted automation while maintaining HIPAA-focused controls.
The project began with workflow analysis and validation before progressing toward a scalable solution. The implementation helped reduce manual documentation effort, received positive feedback from clinical users, and established a roadmap for expansion across additional departments. The client name and identifying details remain confidential.
This experience is relevant to governance platforms because successful healthcare AI requires more than model development. It requires secure data handling, workflow alignment, human oversight, interoperability, and continuous optimization.
For organizations planning to create AI healthcare governance software, PixelBrainy can support the journey from requirements and architecture through AI implementation, integration, deployment, and ongoing improvement.
AI is becoming part of clinical, administrative, operational, and decision-making workflows, making strong governance increasingly important for healthcare organizations. AI healthcare governance software provides a centralized way to manage AI inventories, risk assessments, regulatory compliance, policies, approvals, incidents, evidence, and ongoing monitoring across the organization.
As discussed throughout this guide, the development process of AI healthcare governance software should begin with clear governance requirements and progress through architecture, AI integration, MVP validation, healthcare system integration, security testing, and clinical deployment. Development costs can range from $50,000 to $300,000+, depending on AI capabilities, integrations, security, and enterprise complexity.
Organizations should also evaluate ROI through regulatory risk reduction, credentialing efficiency, policy management, compliance productivity, and survey preparation savings. The right approach is not simply to develop AI healthcare governance software, but to create a secure, scalable, explainable platform that fits real healthcare workflows.
Ready to turn your governance requirements into a scalable AI solution? Book an appointment with PixelBrainy to discuss your project.
The cost to develop AI healthcare governance software can range from $50,000 to $300,000+. A multi-hospital platform usually costs more because of EHR integrations, facility-level workflows, regulatory intelligence, security controls, AI capabilities, data migration, and enterprise scalability.
An AI healthcare governance software MVP should typically include AI asset inventory, risk classification, policy management, compliance workflows, evidence management, approval workflows, audit trails, user permissions, incident tracking, and basic executive reporting. Advanced predictive analytics and complex AI intelligence can be introduced after the core governance workflows are validated.
Yes. AI healthcare governance software development can include integrations with EHR platforms through APIs, HL7, FHIR, SMART on FHIR, and other supported interoperability mechanisms. The integration depth depends on whether the platform only retrieves information or also supports bidirectional governance workflows.
Hospitals can measure ROI through reduced compliance administration, faster credentialing, lower policy management workload, reduced survey preparation costs, improved audit readiness, and avoided regulatory risk. A useful ROI model compares these annual financial benefits against implementation, licensing, integration, infrastructure, and maintenance costs.
Useful capabilities include regulatory document analysis, automated compliance mapping, AI risk assessment, policy comparison, anomaly detection, natural-language governance search, evidence classification, model monitoring, and AI governance assistants. High-impact recommendations should include explainability and appropriate human review.
A basic MVP may take approximately 3 to 6 months, while an advanced enterprise platform can require 6 to 12+ months. The timeline depends on integrations, AI complexity, regulatory workflows, security validation, data migration, customization, and the number of healthcare facilities involved.
The platform should address healthcare data privacy, encryption, role-based access, identity management, audit logging, secure APIs, data retention, vulnerability testing, monitoring, backup, disaster recovery, and appropriate controls for third-party AI services. The exact requirements depend on the data and workflows the platform handles.
Buying can make sense when standard governance workflows meet the organization's requirements and rapid deployment is important. Building custom AI healthcare governance software can be more appropriate when a health system needs complex EHR integrations, multi-facility workflows, proprietary governance logic, specialized regulatory requirements, or deeper control over its technology roadmap.

About The Author
Sagar Bhatnagar
Sagar Sahay Bhatnagar brings over a decade of IT industry experience to his role as Marketing Head at PixelBrainy. He's known for his knack in devising creative marketing strategies that boost brand visibility and market influence. Sagar's strategic thinking, coupled with his innovative vision and focus on results, sets him apart. His track record of successful campaigns proves his ability to utilize digital platforms effectively for impactful marketing efforts. With a genuine passion for both technology and marketing, Sagar continuously pushes PixelBrainy's marketing initiatives to greater success.
Working with PixelBrainy has been a great experience. They took our vision for an AI-powered platform and turned it into a fully functional product. What impressed me most was their strong understanding of both design and development, and their ability to handle complex requirements with ease. The team was responsive, cooperative, and always open to feedback. They kept things organized, communicated clearly, and delivered quality work on time. I highly recommend PixelBrainy to anyone looking for a skilled and reliable development partner.

Working with the PixelBrainy team has been a highly positive experience. They understand the design requirements and create beautiful UX elements to meet the application needs. The dev team did an excellent job bringing my vision to life. We discussed usability and flow. Sagar worked with his team to design the database and begin coding. Working with Sagar was easy. He has the knowledge to create robust apps, including multi-language support, Google and Apple ID login options, Ad-enabled integrations, Stripe payment processing, and a Web Admin site for maintaining support data. I'm extremely satisfied with the services provided, the quality of the final product, and the professionalism of the entire process. I highly recommend them for Android and iOS Mobile Application Design and Development.

Great experience working with them. Had a lot of feedback and I found that unlike most contractors they were bugging me for updates instead of the other way around. They were extremely time conscience and great at communicating! All work was done extremely high quality and if not on time, early! They were always proactive when it comes to communication and the work is great/above par always. Very flexible and a great team to work with! Goes above and beyond to present us with multiple options and always provides quality. Amazing work per usual with Chitra. If you have UI/UX or branding design needs I recommend you go to them! Will likely work with them in the future as well, definitely recommended!

PixelBrainy is a joy to work with and is a great partner when thinking through branding, logo, and website layout. I appreciate that they spend time going into the "why" behind their decisions to help inform me and others about industry best practices and their expertise.

I hired them to design our software apps. Things I really like about them are excellent communication skills, they answer all project suggestions and collaborate right away, and their input on design and colors is amazing. This project was complex and needed patience and creativity. The team is amazing to do business with. I will be using them long-term. Glad to see there are some good people out there. I was afraid to try and outsource my project to someone but I am glad I met them! I really can't say enough. They went above and beyond on this project. I am very happy with everything they have done to make my business stand out from the competition.

It was great working with PixelBrainy and the team. They were very responsive and really owned the project. We'll definitely work with them again!

I recently worked with the PixelBrainy team on a project and I was blown away by their communication skills. They were prompt, clear, and articulate in all of our interactions. They listened and provided valuable feedback and suggestions to help make the project a success. They also kept me updated throughout the entire process, which made the experience stress-free and enjoyable.

PixelBrainy is very good at what it does. The team also presents themselves very professionally and takes care of their side of things very well. I could fully trust them taking up the design work in a timely and organised manner and their attention to detail saved us lots of effort and time. This particular project was quite intense and the team showed that they function very well under pressure. Very much looking forward to working with her again!

It's always an absolute pleasure working with them. They completed all of my requests quickly and followed every note I had for them to a T, which made our process go smoothly from start to finish. Everything was completed fast and following all of the guidelines. And I would recommend their services to anyone. If you need any design work done in the future, PixelBrainy should be your first call!

They took ownership of our requirements and designed and proposed multiple beautiful variants. The team is self-motivated, requires minimum supervision, committed to see-through designs with quality and delivering them on time. We would definitely love to work with PixelBrainy again when we have any requirements.

PixelBrainy was a big help with our SaaS application. We've been hard at work with a new UI/UX and they provided a lot of help with the designs. If you're looking for assistance with your website, software, or mobile application designs, PixelBrainy and the team is a great recommendation.

PixelBrainy designers are amazing. They are responsive, talented, and always willing to help craft the design until it matches your vision. I would recommend them and plan to continue them for my future projects and more!!!

They were awesome! Did a good job fast, and good communication. Will work with them again. Thank you

Creative, detail-oriented, and talented designers who take direction well and implement changes quickly and accurately. They consistently over-delivered for us.

PixelBrainy team is very talented and creative. Great designers and a pleasure to work with. PixelBrainy is an excellent communicator and I look forward to working with them again.

PixelBrainy has a very talented design team. Their work is excellent and they are very responsive. I enjoy working with them and hope to continue on all of our future projects.

Transform your ideas into reality with us.
Across these industries, each engagement brings unique challenges, from early-stage product development to scaling complex systems, helping us build a practical understanding of real-world product environments.